The ChatGPT leak on Google: a wake-up call for enterprise data security
The rapid adoption of generative artificial intelligence in the corporate world has been nothing short of breathtaking. From startups to multinational corporations, teams are leveraging AI algorithms to accelerate content creation, analyze…

Jean-Baptiste DuquesneSEO, GEO & content operations · Published 19 August 2025 · Updated 11 October 2026
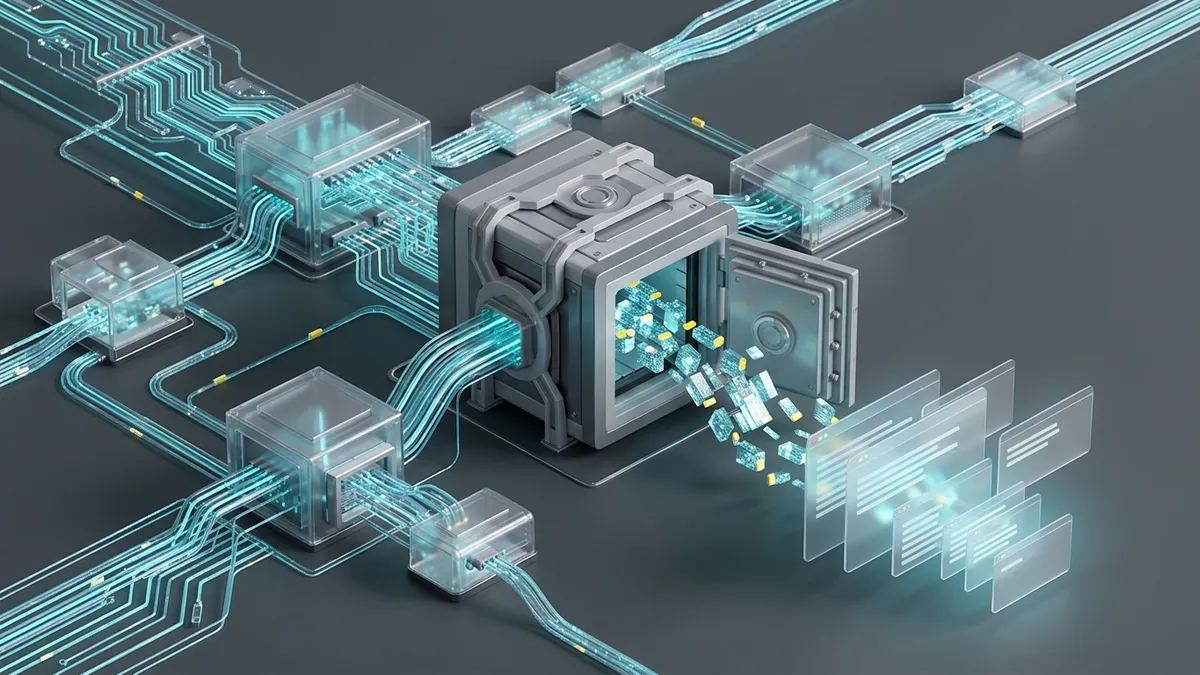
The rapid adoption of generative artificial intelligence in the corporate world has been nothing short of breathtaking. From startups to multinational corporations, teams are leveraging AI algorithms to accelerate content creation, analyze data, and automate workflows. This rush toward productivity, however, has often overshadowed a fundamental and perilous question: where is our data going?
A recent, high-profile incident brought this question into sharp focus: the discovery that private user conversations from ChatGPT had become publicly searchable via Google. This leak was not a malicious hack, but a configuration issue. This event is a blaring wake-up call regarding the profound risks of using third-party AI tools for proprietary information.
The anatomy of a leak: what actually happened
At the heart of the leak was the "Share" button, a feature designed for collaboration. This option allows users to generate a unique URL for their conversation. However, these shared URLs were public and lacked a noindex directive, meaning Google's crawlers could index them. Businesses must realize that AI tools often prioritize convenience over security in their default settings.
The impact was immediate. If employees used the link feature to share internal brainstorming, they unknowingly bypassed the corporate firewall. As specialized tools like Google Vids arrive in Google Workspace, teams must remain vigilant about how collaborative AI features handle sensitive information. This incident serves as a terrifying proof of concept for how security oversights can damage brand credibility.
The enterprise dilemma: productivity vs. risk
ChatGPT offers immediate productivity gains, but at a hidden cost. When employees use public services, the company loses control over its data. This risk is particularly high as ChatGPT integrates Outlook and other workplace applications, potentially exposing sensitive email communications to AI processing. This is why many companies are now adapting their brand strategy to AI to include strict security protocols. Every prompt entered represents a transfer of intellectual property to an external environment that is outside the company's control.
Banning AI is not a viable long-term strategy, as it creates a competitive disadvantage. Instead, companies must address AI as an organizational challenge by defining clear policies. Governance is the only path forward. Educating teams on the risks of AI API integrations and public prompts is the first step toward a safer digital ecosystem. While protecting privacy is paramount, many leaders are evaluating the security and privacy of data in their infrastructure, often weighing the benefits of cloud vs local AI solutions.
Toward a "zero trust" AI paradigm
The zero trust principle dictates that no entity should be trusted by default. This mindset must extend to AI. Companies need to build a "walled garden" to protect their assets. This involves creating a buffer between employees and external models to ensure that brand consistency is maintained without risking data leaks during the creative process.
By implementing a structured AI governance model, firms can manage outputs securely. Sensitive data should be anonymized, and prompts monitored. The goal is to maximize marketing efficiency while ensuring the final assets are stored within internal systems.
Advanced governance for the AI era
To stay ahead, organizations are turning to AI agents that operate within controlled parameters. These agents can perform tasks while strictly adhering to privacy settings. Furthermore, using AI clustering techniques on internal data can help identify where sensitive info exists before it is ever sent to an LLM for processing.
Preparation is key for the future of work. Data literacy and security awareness are now mandatory competencies. Finally, companies must be wary of the media traffic drop caused by AI Overviews, which makes owning and securing your primary or proprietary content even more valuable.
How Brandeploy secures your AI content and brand assets
Brandeploy is a creative automation and brand management platform that helps enterprise teams scale content production while maintaining total control over their data. We act as a secure central vault for all brand assets, ensuring a sharp separation between the AI experimentation phase and your official repositories. By integrating your brand guidelines into a managed workflow, we prevent sensitive information from remaining on external platforms like ChatGPT. Brandeploy provides the essential governance framework to keep your intellectual property safe and consistent across all markets. To see how we can protect your brand, book a demo of our platform today.
FAQ
What caused the ChatGPT data leak on Google?
The ChatGPT leak was caused by an indexing issue where shared conversation URLs lacked a noindex directive. This allowed Google's web crawlers to discover and index thousands of private chat links. Anyone using specific search queries could find and read these conversations, highlighting a major AI security flaw in how public AI tools handle shared data links.
What are the main security risks for companies using ChatGPT?
Businesses risk exposing intellectual property, trade secrets, and customer data when using public AI tools. If employees share chat links or input sensitive code, that data can be indexed by search engines. Establishing a robust AI marketing model and governance framework is essential to prevent unauthorized access to proprietary assets stored on third-party servers.
How can organizations protect their data from AI leaks?
To secure corporate data, organizations should implement a zero trust AI strategy. This includes using enterprise-grade AI versions with data protection agreements, anonymizing prompts, and utilizing a centralized platform for asset management. It is crucial to move away from public "free" tools toward controlled environments that prevent internal data from leaking into the public domain.
What is a "walled garden" in the context of enterprise AI?
A "walled garden" approach involves creating a secure, internal environment where AI tools are used under strict supervision. This setup ensures that AI and content creation occur within a protected infrastructure. By decoupling the AI model from the storage of final assets, companies can leverage generative power while maintaining 100% control over their intellectual property.
Should companies ban AI tools to avoid data leaks?
No. Banning AI is not a viable long-term strategy, because it creates a competitive disadvantage. Companies should treat AI as an organizational challenge and define clear policies for its use. Governance is the only path forward. Educating teams on the risks of AI API integrations and public prompts is the first step toward a safer digital ecosystem.
Written by
Jean-Baptiste Duquesne
SEO, GEO & content operations
Web pioneer since 1995, founder of the recipe site 750g.com (sold to Webedia), now industrialising SEO and GEO content production with AI.
Ready to scale your content production?
Book a demo